Why Smart Business Leaders Are Asking Different Questions About IT
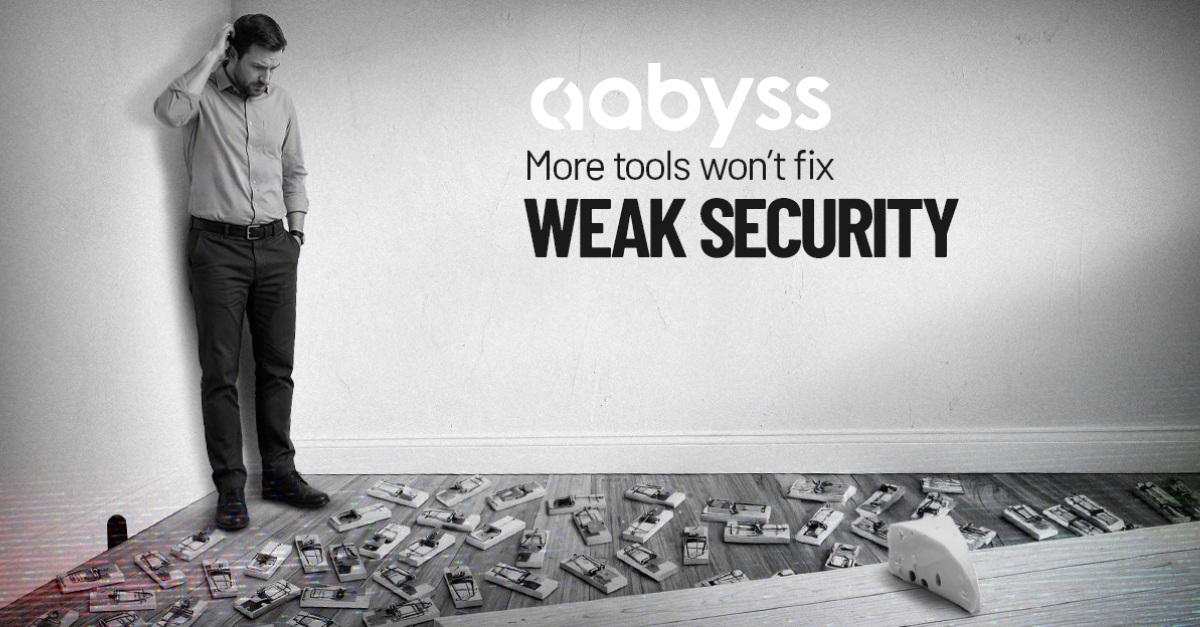
When business leaders start reviewing their cyber security, the conversation often turns to technology. Should we add another security platform? Do we need another monitoring tool? Would another product make us safer?
It's an understandable way of thinking. More protection should mean less risk. Unfortunately, cyber security doesn't work like that.
In fact, one of the most common problems we see when businesses review their current IT provider is an environment filled with tools that have been added over time without a clear strategy behind them. The result? More complexity. More cost. More confusion. And often, more risk.
The Cyber Security Myth That Costs Businesses Money
Many businesses believe security is a numbers game. More software. More dashboards. More licences. More alerts. But every new tool introduces another system to manage, another configuration to maintain and another source of information to review.
The question is not: "How many security tools do we have?"
The question is: "Do we know how effectively they're working together?"
Because a business with ten poorly managed security tools is rarely safer than a business with five well-managed ones.
Complexity Is The Enemy Of Good Security
Most businesses don't intentionally create complicated IT environments. It happens gradually. A backup solution is added. Then an email security platform. Then a monitoring tool. Then a password manager. Then another security service was recommended by a supplier.
Each solution addresses a genuine concern. Over time, however, nobody reviews how everything fits together. Business leaders are left paying multiple suppliers and multiple subscriptions while becoming less certain about their actual level of protection.
When security becomes difficult to understand, it becomes difficult to manage. And unmanaged security creates risk.
More Alerts Don't Mean More Security
One of the biggest side effects of a growing security stack is alert overload. Every tool wants attention. Every platform generates notifications. Every report claims importance. At first, this feels reassuring. Eventually, it becomes noise.
When teams are overwhelmed by hundreds of notifications, genuine threats become harder to identify. This is known as alert fatigue. The danger is not a lack of information.
The danger is having so much information that critical warnings get overlooked. Good security should create clarity. Not confusion.

Duplicate Tools Create Duplicate Costs
Many businesses are surprised when they take a closer look at their security spend. It's common to discover multiple tools performing similar functions. Different suppliers. Different contracts. Similar outcomes. Not only does this create unnecessary costs, it creates operational uncertainty.
When a security incident occurs, which tool should be trusted? Which report is accurate? Which platform takes priority? These are questions that should be answered long before a security incident occurs. A well-managed security strategy removes overlap and gives every tool a clearly defined role.
A Security Tool Is Only Effective When It's Managed Properly
One of the most dangerous assumptions in cyber security is believing that buying a tool solves the problem.
Technology isn't a set-and-forget purchase.
Businesses change. Employees join and leave. New systems are introduced. Threats evolve. Security tools need reviewing, maintaining and adapting to keep pace.
A perfectly good security platform can become ineffective if it's not configured properly or regularly reviewed. The issue isn't normally the technology itself. The issue is whether someone is actively managing it.
What Business Leaders Should Be Asking Their IT Provider
If you're considering changing IT providers, don't focus on how many security products they can sell you. Ask them:
- Why do we need each tool?
- What risk does it address?
- How does it integrate with the rest of our security strategy?
- Are we paying for overlapping services?
- How do we know our current tools are working as intended?
A good IT provider should simplify security, not make it more complicated.
Strategy Beats Quantity Every Time
The businesses with the strongest cyber security are not necessarily the ones with the biggest technology stacks. They're the ones with a clear strategy. They understand what they're protecting. They know where their biggest risks exist. They regularly review their protections. And they ensure every tool has a purpose.
Think of your security stack like a leadership team. Adding more people doesn't automatically improve performance. Success comes from making sure everyone has a clear role, understands their responsibilities and works towards the same objective. Cyber security is no different. The best security stack isn't the largest.
It's the one where every tool earns its place.
Is Your Security Stack Protecting Your Business Or Complicating It?
If you're reviewing your current IT provider, now is the perfect time to take a fresh look at your security environment. You may discover you're paying for tools you don't need. You may discover gaps you didn't know existed. Or you may simply find opportunities to make security more effective and easier to manage.
Book a quick, no-obligation discovery call using the scheduler on this page and let's find out whether your current security tools are reducing risk or adding complexity.
 Aaron Hayes.

 Aaron Hayes. : May 18, 2026, 3:10:37 PM

